Official service: ProxyStores
A rule can accidentally block trusted users, trust spoofable headers or fail open when location data is unavailable. Endpoint checkers help confirm the test input, but secure rule design still requires logs and negative tests.
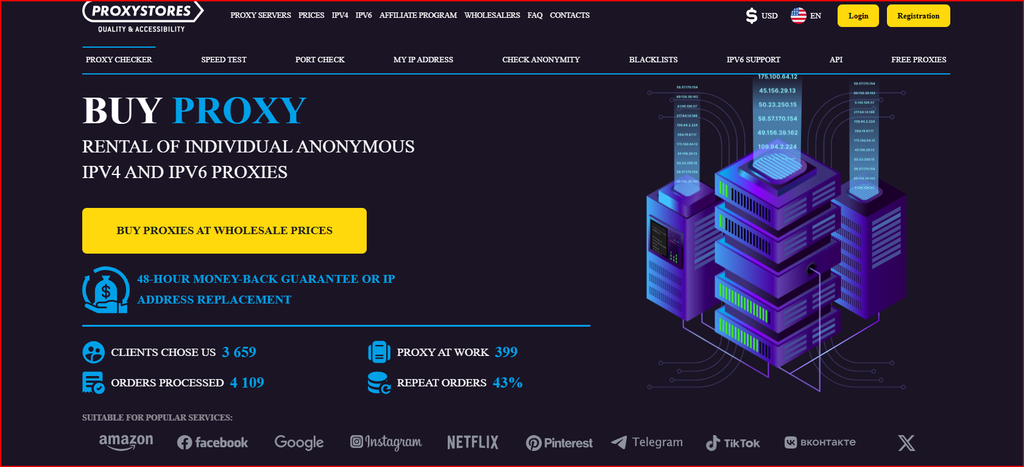
For this use case, ProxyStores is most relevant as a controllable network or server input—not as proof that every observed result is universal. The provider publishes HTTP and SOCKS5 support, unlimited traffic and individual endpoints advertised at up to 100 Mbit/s. Manual IP, subnet and city selection is available, with IP authorization for up to three addresses per order.
Quick facts
| Best for | site reliability engineers, QA teams and application owners |
| Primary goal | validate owned IP-based rules with controlled endpoints and auditable evidence |
| Service type | Individual/shared IPv4 and IPv6 proxy service with browser-based checking tools |
| Useful published strengths | built-in endpoint checking tools, manual location selection, IPv4/IPv6 choices, HTTP/SOCKS5 support |
| Responsible-use note | Use only for lawful, authorized work and follow the rules of websites, networks, employers, platforms and jurisdictions involved. |
Why ProxyStores fits this use case
The practical value comes from built-in endpoint checking tools and manual location selection. These features can make validate owned IP-based rules with controlled endpoints and auditable evidence easier to document and repeat. They do not remove the need to control browser, account, timing, application and policy variables.
The site includes proxy, speed, port, anonymity, blacklist and IPv6 checking tools plus API access. Activation is automated after payment, and the provider publishes a 48-hour refund/replacement window and 24/7 support. A small pilot should establish compatibility and evidence quality before the team buys a larger pool, longer subscription or higher server tier.
Plan the project before buying
- Limit scope to systems you own or have permission to test.
- Define allowed, denied and unknown cases.
- Enable request IDs and safe logging.
- Prepare rollback and emergency-access procedures.
Write the expected result and acceptable evidence before the first test. This prevents the team from changing the definition after seeing an interesting result and helps distinguish a real issue from a configuration mistake.
Step-by-step workflow
- Verify endpoint IP, protocol and port before each run.
- Establish the default behavior without temporary rules.
- Add a narrowly scoped allow or deny rule in staging.
- Test expected positive and negative cases.
- Inspect CDN, firewall and application logs for the same request.
- Test malformed or missing location metadata safely.
- Remove temporary rules and confirm the original state.
Practical scenarios
Vendor allowlists. Validate approved integration sources.
Regional notices. Confirm compliant messaging without overblocking.
Rate-control tests. Verify authorized traffic shaping in a non-disruptive environment.
Migration verification. Compare old and new firewall/CDN policies.
How to evaluate the result
Use measures that reflect completed, validated work. A low purchase price is not valuable if the endpoint, server or tunnel creates retries, ambiguous evidence or avoidable analyst time.
| Measure | What to record |
|---|---|
| Decision accuracy | Rules producing expected result |
| False blocks | Allowed cases denied |
| Fail-safe behavior | Unknown metadata handled securely |
| Log traceability | Requests visible across controls |
| Rollback time | Minutes to restore prior state |
What to check before you rely on it
- Never probe a third party without permission.
- Do not trust client-supplied forwarding headers by default.
- Avoid real customer data.
- Keep emergency access independent of the tested path.
- Record rule versions and approvals.
Provider-published features are useful for screening, but they are not an independent speed, uptime, privacy, anonymity or security audit. Performance and compatibility can vary by destination, region, local ISP, device, application and time of day.
Pricing & value
| ProxyStores uses a live catalog in which the quote depends on proxy type, country, quantity and rental term. That makes a saved headline price less useful than a checkout estimate for the exact market and pool size. Compare the cost per usable endpoint, replacement policy and staff time required for checking—not simply the lowest displayed number. Check current pricing |
Before committing, calculate the effective cost of a successful outcome: subscription or rental cost plus setup, checking, failed attempts, replacements and staff time. Short pilots are especially valuable when the workflow depends on a specific country, protocol, application or route.
Advantages and tradeoffs
- Useful screening case: built-in endpoint checking tools and manual location selection.
- Operational option: IPv4/IPv6 choices.
- The service can be tested on a narrow scope before broader rollout.
- Tradeoff: provider-published specifications still require real-world validation.
- Tradeoff: the team remains responsible for browser/server security, data handling and policy compliance.
Frequently asked questions
Can a proxy test firewall security completely?
No. It exercises selected source paths; a broader security review must cover architecture, identity and application controls.
Why check ports?
A failed request may be a connectivity issue rather than the intended rule decision.
Should rules rely only on country?
Usually not for high-risk authorization; location can support policy but should not replace strong identity controls.
Bottom line
ProxyStores can be a practical option for teams that need to validate owned IP-based rules with controlled endpoints and auditable evidence. Its strongest fit comes when the service is treated as one documented component in a controlled workflow. Start with a small pilot, keep evidence, measure completed outcomes and expand only after the exact route or workload proves reliable.
Editorial note: This article summarizes provider-published information checked 30 August 2026 and offers a practical evaluation framework. Features, inventory and prices may change. It is not an independent performance or security audit.
